National Security Strategy 2025
Government are updating its war plans for threats to the UK mainland.
The national direction has changed
“We must also now mobilise every element of society towards a collective national effort.”
The national direction has changed
“We must also now mobilise every element of society towards a collective national effort.”

The UK is currently developing a series of programmes to increase defence readiness. This follows NATO Article 3, Cyber Security and Resilience Bill and the proposed legislation on defence readiness and national resilience.
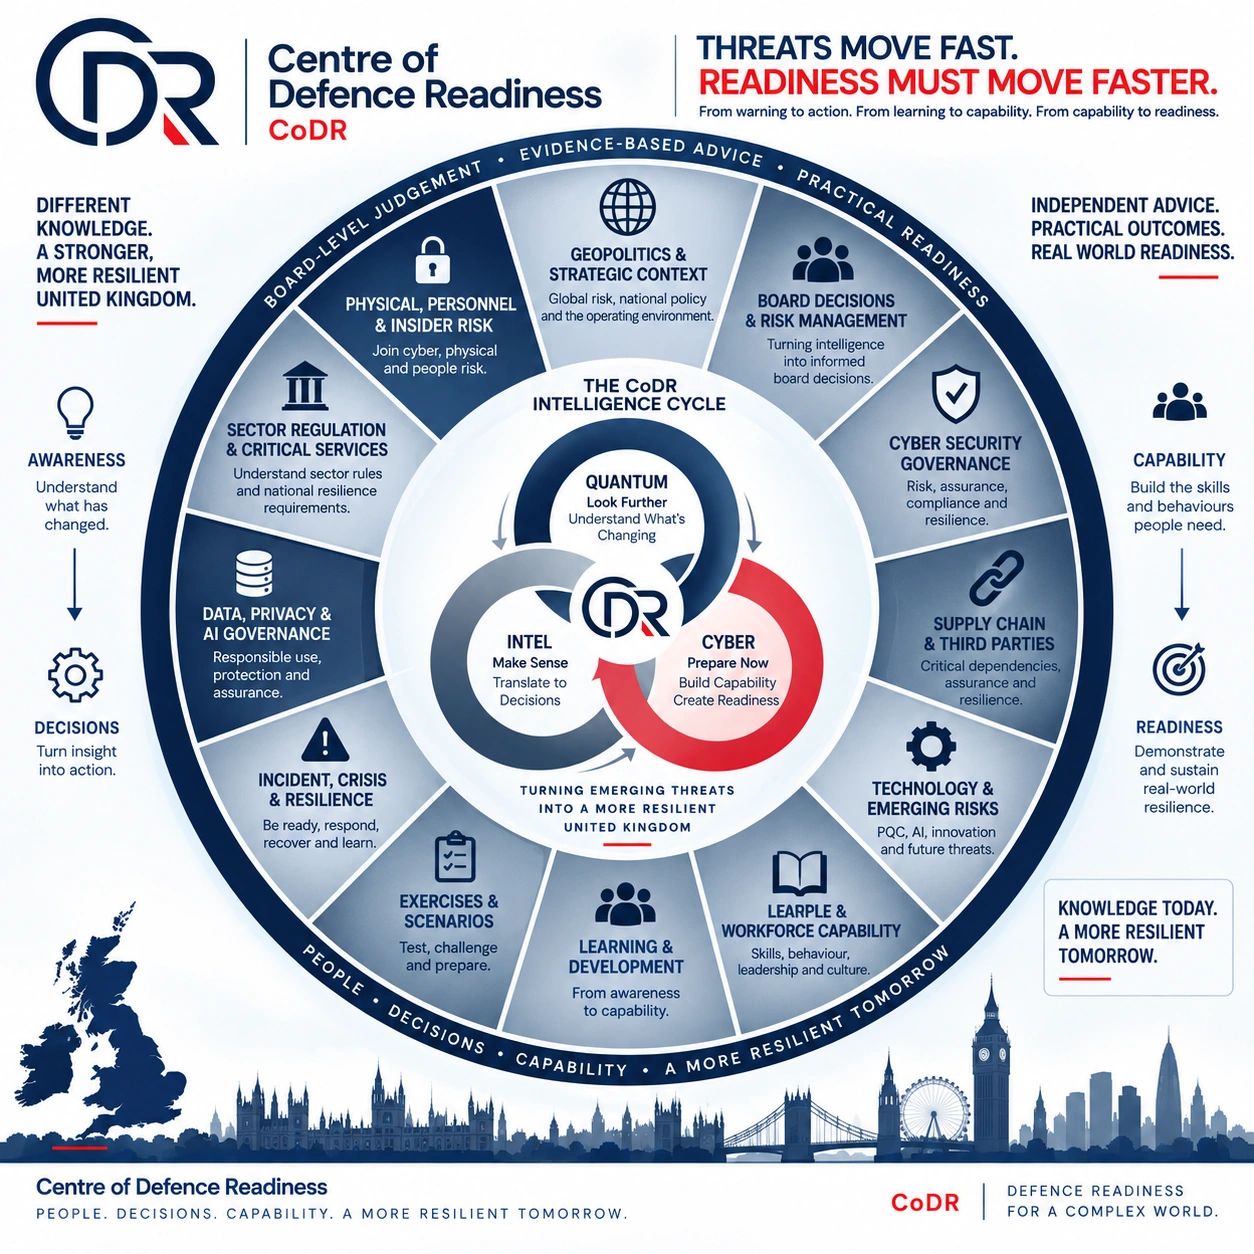
National defence depends not only on the Armed Forces, but on the organisations that sustain economic capacity, essential services and military operations through conflict-level disruption. CoDR closes the gap between strategic warning and organisational action.
Build organisational resilience and ensure continuity of critical functions by proactively reducing the probability of risk.
Readiness depends on knowing what must continue, what the organisation relies on and where disruption can cascade .
Clear authorities and realistic exercises build the judgement and reflexes needed for crisis, mobilisation and national support.
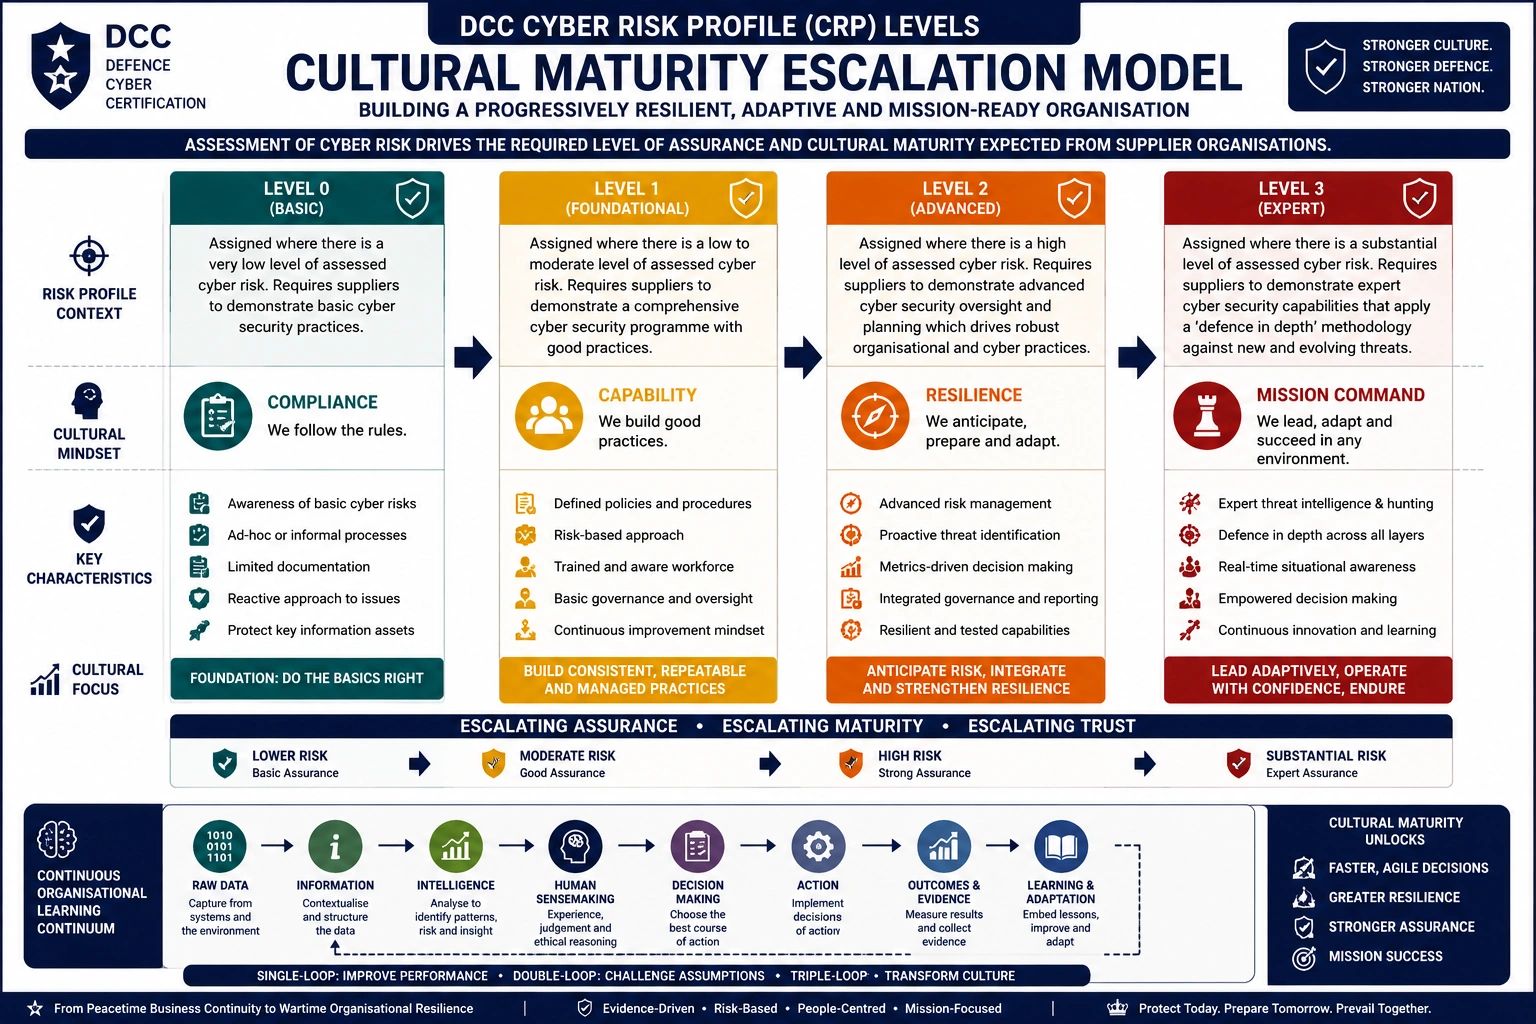
Awareness → doctrine → systemic context → rehearsal → integration. Each stage creates the shared language, evidence and decisions that the next stage can test.
This provides a baseline understanding of your cyber protection. Split in two level.
This provides a defence supply-chain assurance. Split into three levels.
GovAssure is the cyber security scheme for assessing government critical systems.
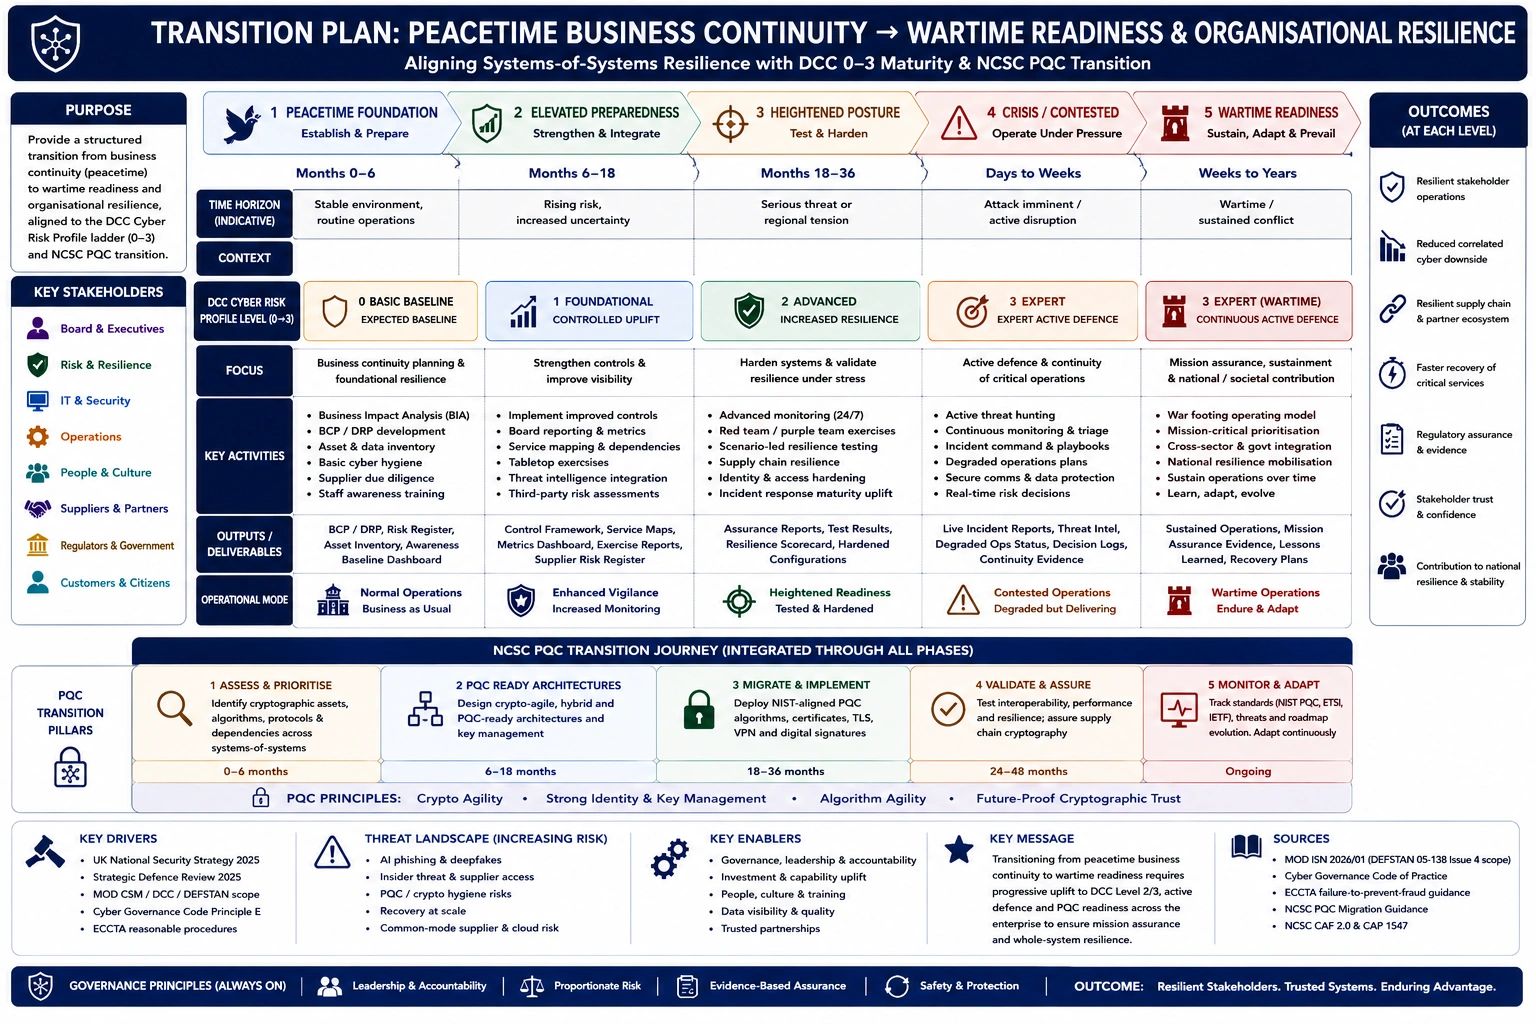
Conventional continuity plans assume a bounded incident, available suppliers and a return to normal. Defence readiness asks whether essential outcomes can continue through simultaneous, sustained and adversarial disruption.
Leaders define the mission, set risk appetite and decide which trade-offs the organisation can accept.
Readiness depends on knowing which suppliers, systems, infrastructure and people sustain essential outcomes.
Clear authorities and realistic rehearsal give leadership teams the judgement to act under pressure.

CoDR works with leaders whose organisations support essential services, defence capability or critical supply chains. The key question is whether the mission can continue when pressure is sustained and dependencies fail together.
Prime contractors, strategic suppliers and organisations working under defence security and resilience expectations.
Data centres, cloud providers, managed services, telecommunications and identity-dependent services.
Operators whose disruption would create wider social, economic or national consequences.
Quantum 4sight is a secure mission digital-twin platform for rehearsing cyber, physical-security and operational incidents in a realistic representation of your organisation.
It connects critical services to the people, systems, facilities, suppliers and infrastructure that sustain them.
Participant decisions influence what happens next, exposing hidden dependencies and producing structured evidence for resilience improvement.
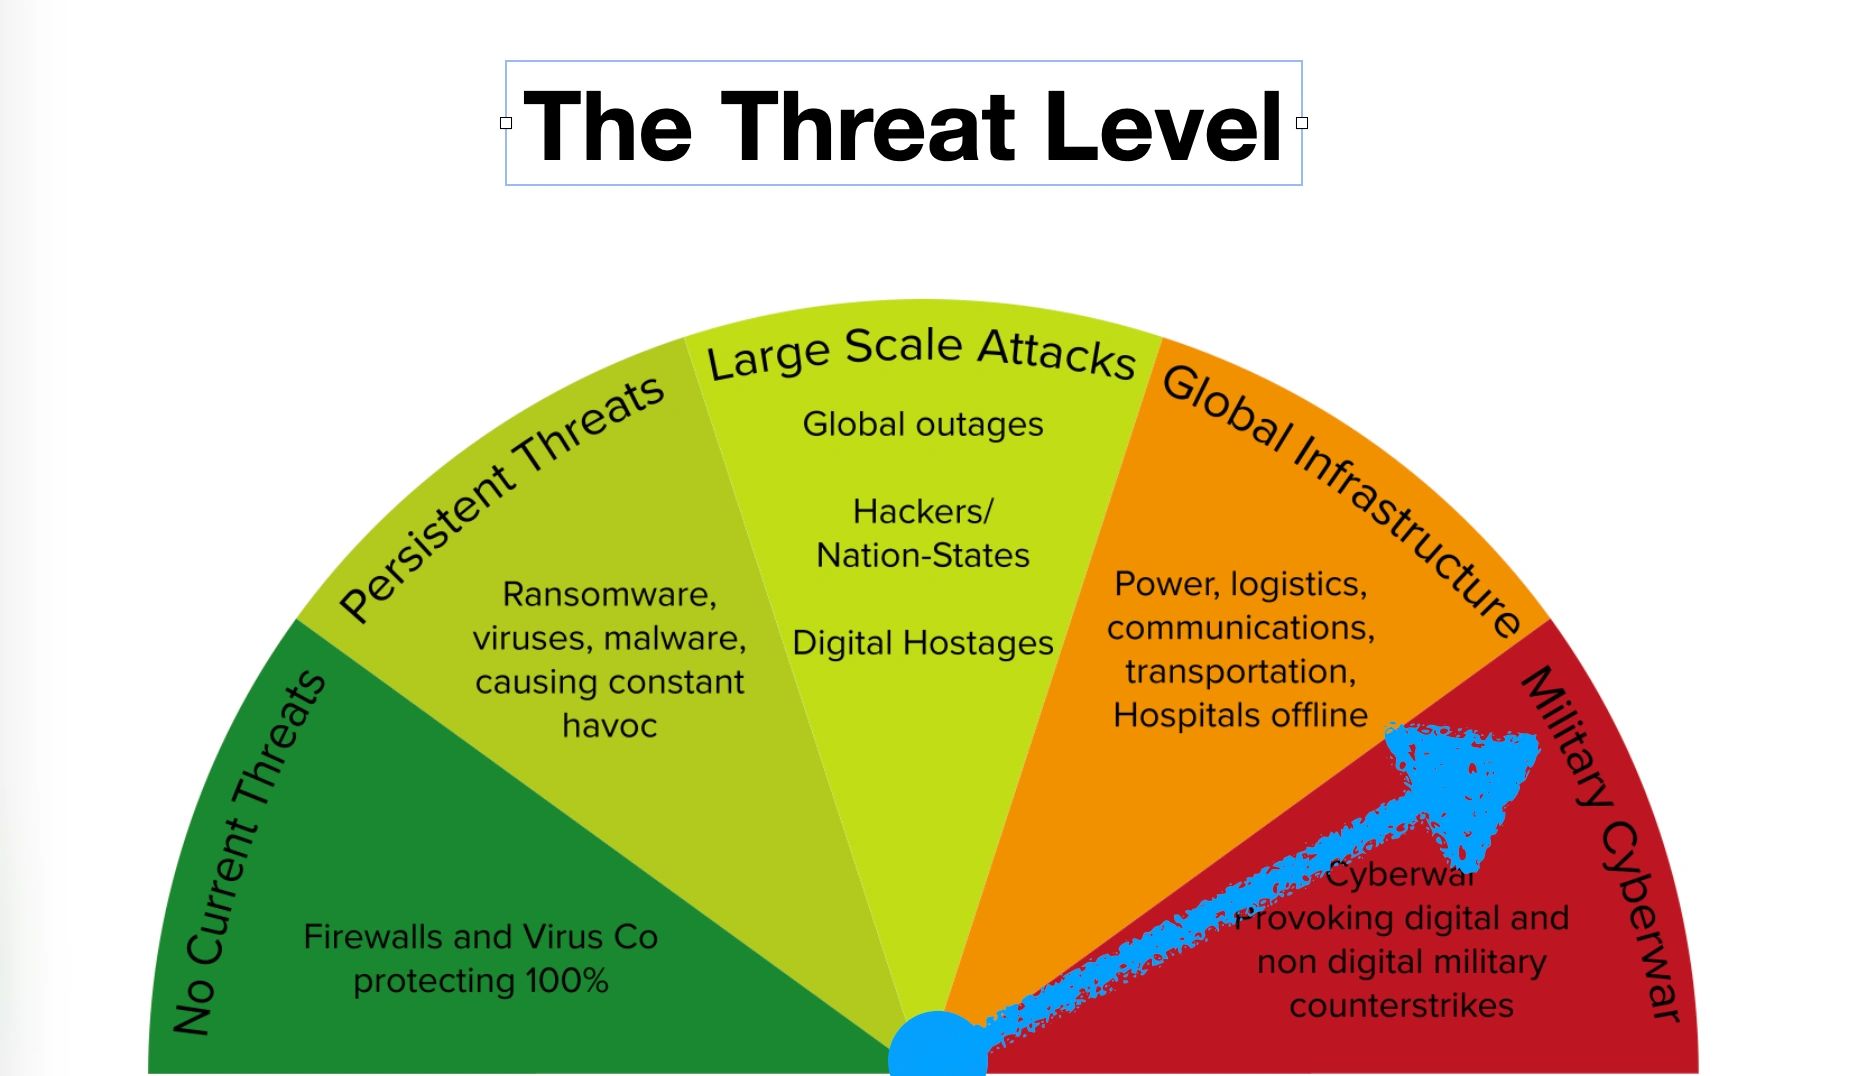
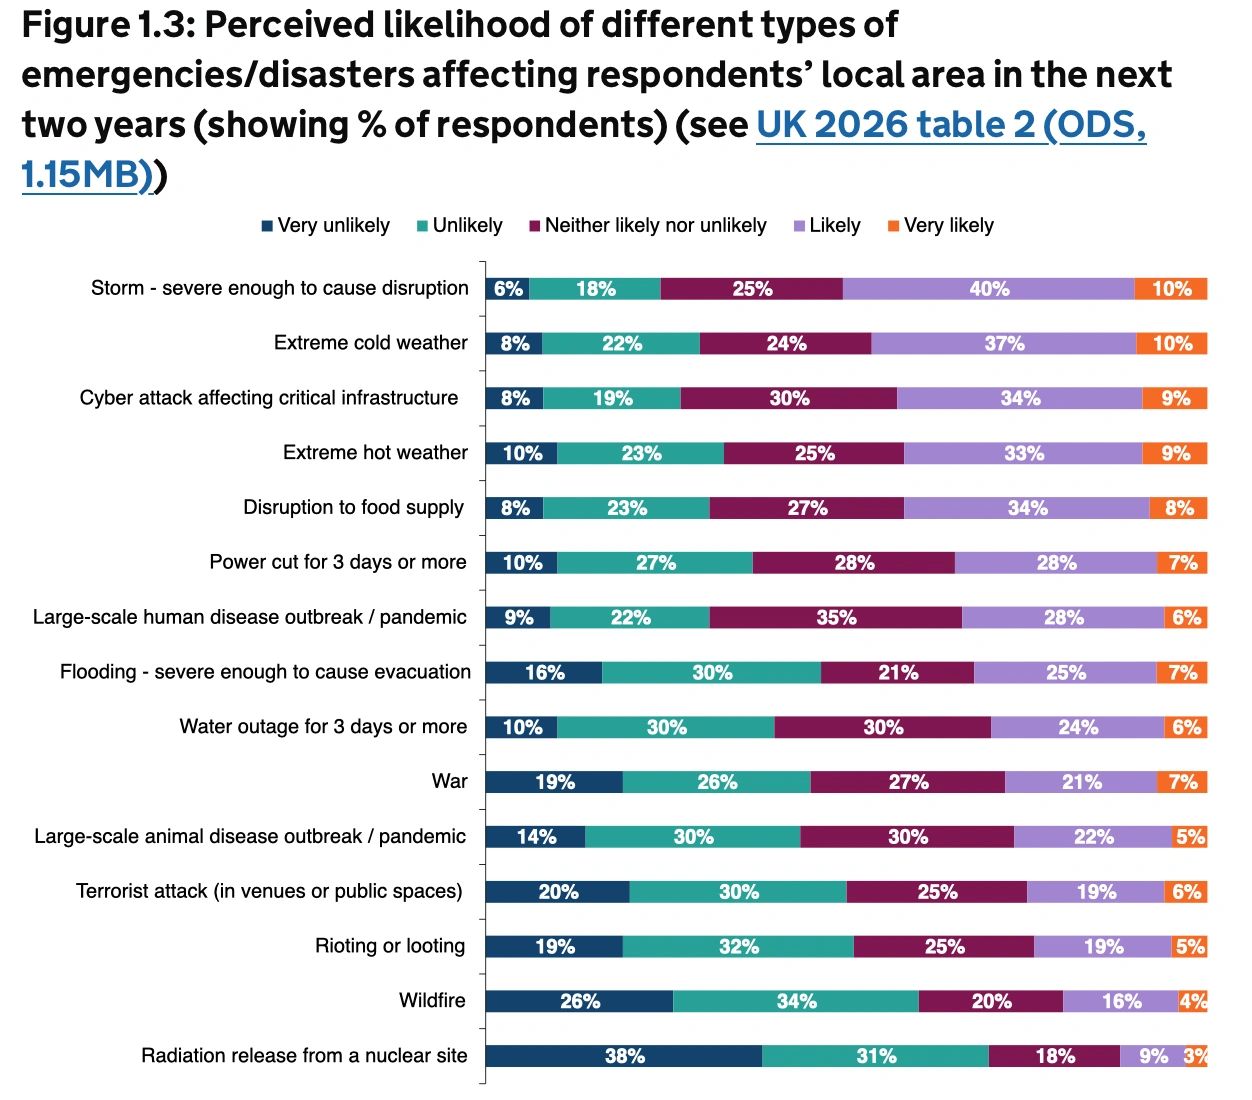
Which outcomes must continue? Could separate incidents form one strategic problem? Which dependencies sit outside your control? Are decision rights clear? What evidence shows leadership has rehearsed?
Use pattern, timing, target, dependencies and effects to assess a campaign without overstating attribution.
Separate fact, assessment, assumption and decision so the board understands both the evidence and its limits.
The session produces a shared threat model, stronger board questions and one owned action leading into Course 2. It is defensive and public-evidence based, not intelligence or certification.
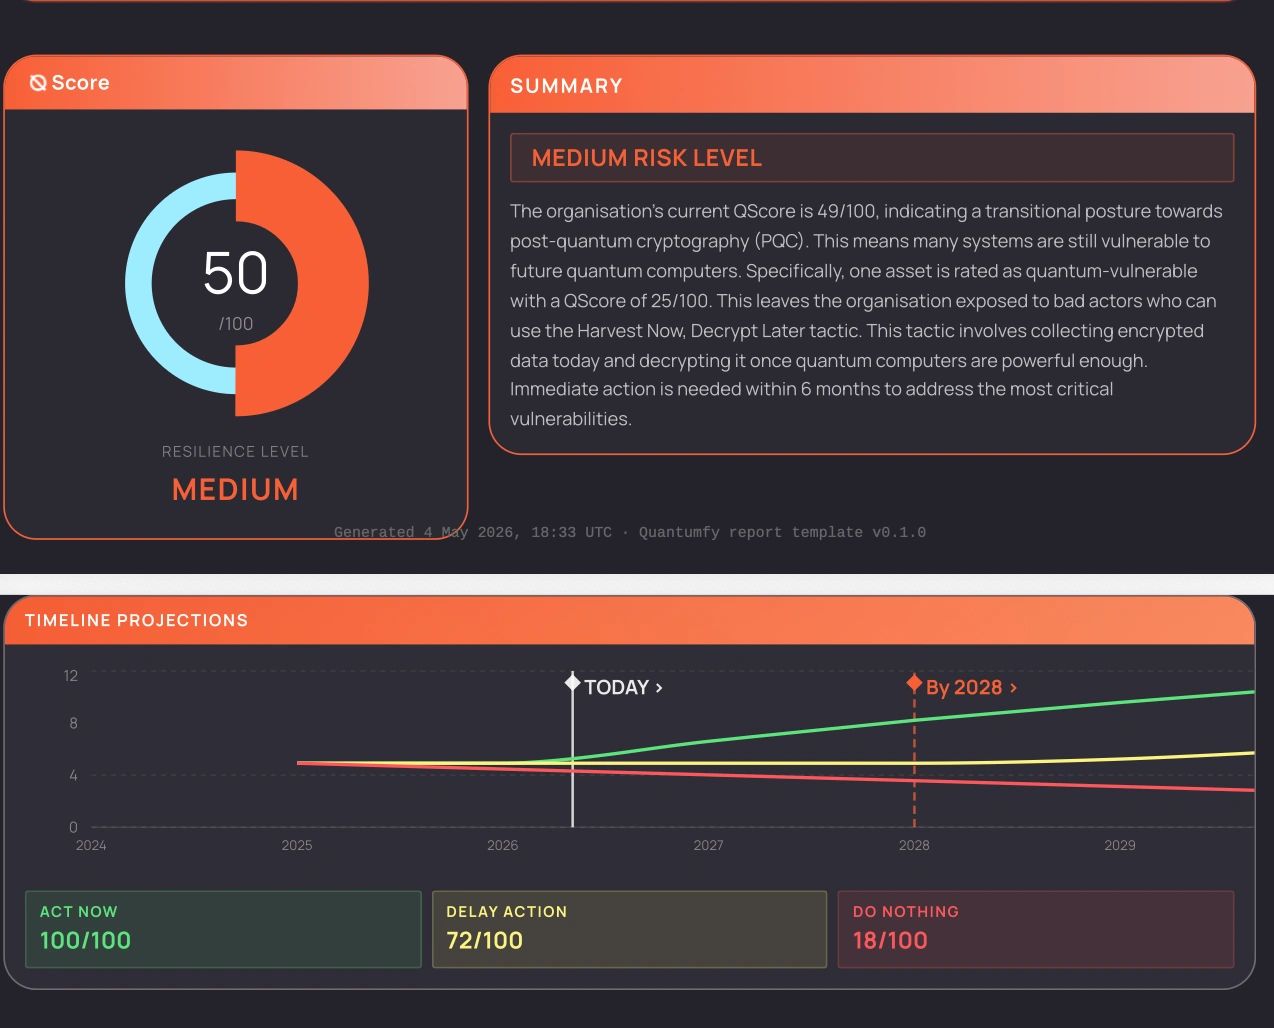
Sensitive information can be collected now for later decryption. Boards need clear ownership, evidence of cryptographic exposure and a funded migration path before quantum-vulnerable dependencies become urgent.
PQC affects confidentiality, identity, signatures, software integrity, supply-chain assurance and systems with long service lives.
Cryptography sits across identity, software updates, operational technology, cloud services and supplier products.
Name an accountable executive, define the assessment boundary and give the work enough authority and resource to establish a defensible baseline.